Domain names and top-level domains are two levels of one addressing system. A domain name such as www.example.com is a string of labels separated by dots, and each label is a step down a hierarchy that starts at an unnamed root, passes through a top-level domain such as .com, and ends at the name of a specific host. The Domain Name System, or DNS (the internet’s distributed directory), walks that hierarchy from right to left to find the IP address (Internet Protocol address, the numeric address computers actually use to connect) of the server behind the name. This guide explains how that internet addressing works: what a label is, how the hierarchy is organized, what the root does, and how a name becomes a number.

Two Kinds of Internet Address
The internet runs on numbers. Every server, router and phone that sends or receives traffic has an IP address. An IPv4 address is 32 bits long and written as four numbers, such as 192.0.2.10. An IPv6 address is 128 bits long and written in hexadecimal groups, such as 2001:db8::10. Routers move packets using these numbers alone; they never see a domain name.
Domain names exist for people. They are easier to remember than numbers, and they stay the same when the number behind them changes. A business can move its website to a new hosting company, receive a completely new IP address, and keep the same domain name, because only the DNS record that links the two needs to change. That separation between the name people use and the number machines use is the central idea of internet addressing, and the rest of this guide builds on it.
The two kinds of address are also managed by different systems. IP addresses are allocated by IANA (the Internet Assigned Numbers Authority) to five regional internet registries, such as ARIN for North America and RIPE NCC for Europe, which assign them to internet providers and large networks. Domain names are allocated through registries and registrars under policies set by ICANN (the Internet Corporation for Assigned Names and Numbers). Owning a domain name gives you no IP address, and holding an IP address gives you no domain name.
Labels: The Building Blocks of a Domain Name
Each part of a domain name between the dots is called a label. In www.example.com there are three labels: www, example and com. The DNS standards set a few rules for labels. Each label can be up to 63 characters long, and a full name can be up to 253 characters. Traditional hostnames use only letters, digits and hyphens, and a label cannot begin or end with a hyphen. Labels are not case-sensitive, so Example.COM and example.com are the same name.
Names in other scripts, such as Arabic, Chinese or Cyrillic, are handled through internationalized domain names, or IDNs. The characters a person sees are converted into an ASCII form that begins with “xn--” before DNS ever processes them. That conversion is why a name can look like one thing in a browser bar and be stored as something quite different in the registry, and it is also why attackers can register names that look identical to a real brand using characters from another alphabet.
The Hierarchy: Reading a Domain Name From Right to Left
A domain name is read from right to left, from the most general label to the most specific. The diagram in most textbooks is an upside-down tree. At the top is the root. Below the root are the top-level domains. Below each top-level domain are the second-level domains that people register, and below those are any subdomains the owner creates.
Take shop.example.com as an example. The label com is the top-level domain, or TLD. The label example is the second-level domain, registered by its owner through a registrar. The label shop is a subdomain that the owner created without registering anything new, simply by adding a DNS record. Each level controls only the level directly beneath it. The .com registry decides who holds example.com, and the holder of example.com decides what shop.example.com points to. This pattern of handing control down one level at a time is called delegation, and it is what lets a single global system run without a single global operator.
Technically, every fully qualified domain name ends with one more dot, written as www.example.com. with a trailing period. That final, empty label is the root. Browsers and email programs add it silently, which is why most people never see it.
The Root Zone and the Root Servers
The root zone is the list at the very top of the hierarchy. It contains one entry for each top-level domain, and each entry names the servers that are authoritative for that TLD. IANA manages the content of the root zone under ICANN’s oversight, and the root zone file is distributed by root server operators around the world. The root zone is short by DNS standards: the European Commission’s Joint Research Centre counted 1,494 TLDs in the root zone as of October 2021, of which 1,377 were signed with DNSSEC, according to its 2022 analysis of DNSSEC uptake in the EU.
The root servers answer one kind of question: where to find the servers for a given TLD. There are 13 named root server identities, labeled A through M and run by a dozen independent organizations, but each identity is served from many locations at once through anycast (a routing method that sends a query to the nearest of many servers sharing one address). The root servers do not know where example.com is. They only know who runs .com, and that is all they need to know.
Top-Level Domains in the Addressing System
Top-level domains are the first level below the root, and each one is run by a registry that keeps the authoritative list of names registered in it. Generic TLDs such as .com, .net and .org are open to registrants worldwide. Country-code TLDs, such as .us, .uk and .de, use two-letter codes and are run under rules set by each country’s designated manager. The newer generic TLDs, such as .art, .gallery, .photography and .bank, were added through ICANN’s new gTLD program, which had delegated over 1,200 new gTLDs by 2021, according to WIPO document SCT/48/2.
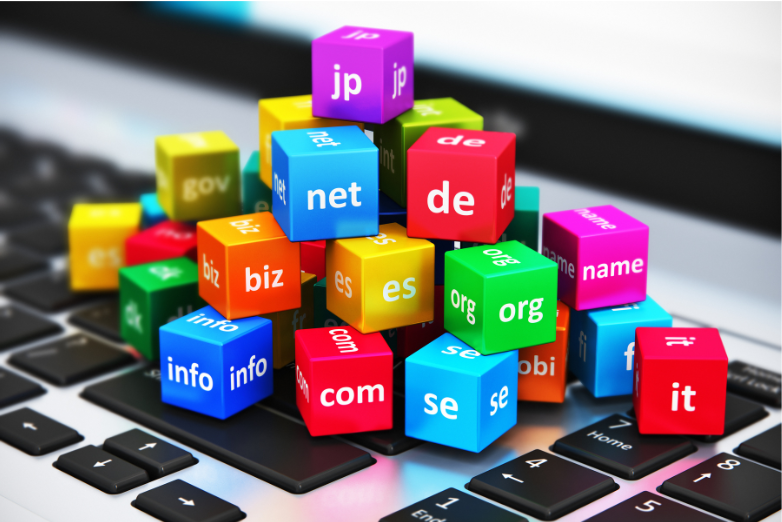
Registrations remain concentrated in a few TLDs. At the end of 2025, .com held 161.0 million registrations and all country-code TLDs together held 145.6 million, out of 386.9 million across every TLD, according to Verisign’s Domain Name Industry Brief release for the fourth quarter of 2025.
From an addressing point of view, the extension a business chooses changes who operates its zone and which rules apply, not how the name resolves. A .art name and a .com name are found in exactly the same way. Industry-specific extensions can help with branding, but they do not carry any special ranking advantage in search engines. Our guide to top-level domains compares the TLD families, explains sponsored and brand TLDs, and covers how to choose an extension for a business.
How a Domain Name Becomes an IP Address
The lookup that turns a domain name into an IP address is called resolution, and it follows the hierarchy exactly. Suppose a browser needs the address of www.example.com. First, the device asks a recursive resolver, usually run by the internet provider or by a public service such as Google Public DNS or Cloudflare’s 1.1.1.1. If the resolver has the answer in its cache, it replies immediately. If not, it asks a root server where to find .com. The root server refers it to the .com servers. The resolver then asks a .com server where to find example.com, and that server refers it to the nameservers the owner set at the registrar. Finally, the resolver asks those authoritative nameservers for the address of www.example.com, receives an A record (for IPv4) or AAAA record (for IPv6), and passes the answer back to the browser.
Each answer carries a TTL (time to live, the number of seconds a resolver may cache it), so most lookups never reach the root at all. Caching is why DNS changes take time to appear everywhere, and it is also why the resolver a person uses matters. About 85% of internet users rely on their internet provider’s default resolvers, and only about 30% of users sit behind resolvers that perform DNSSEC validation, according to Geoff Huston’s September 2023 APNIC measurement of DNSSEC queries. Our guide to how DNS translates domain names walks through each step of resolution in more detail.
Who Runs Each Level
The hierarchy of names is matched by a hierarchy of responsibility. ICANN sets policy for generic TLDs and coordinates the root. IANA maintains the root zone. Each registry operates one or more TLDs and their authoritative servers. Registrars sell registrations, pass the owner’s instructions to the registry, and record which nameservers a domain uses. The registrant, the person or organization that holds the domain, decides what records the domain publishes, usually through a DNS host that may or may not be the same company as the registrar.
That chain explains why control of a domain sits in the registrar account. The registry trusts the registrar, and the registrar trusts whoever logs in to the account. Our guide to the difference between a registrar and a registry explains how a change moves from one to the other, and our guide to nameservers and DNS records explains the records each domain publishes.
Where Internet Addressing Breaks
Because each level trusts the level above it, a domain can be redirected without anyone touching the website. If an attacker changes the nameservers at the registrar, every resolver in the world will follow the new delegation to servers the attacker controls. That is DNS hijacking, and it can take a website and all of a company’s email at once. Our guide to DNS hijacking explains how these attacks work and how to detect them.
Delegation can also fail quietly. When a domain’s nameservers point to a host name that later lapses, anyone who registers that host name can answer for the domain. ICANN’s Security and Stability Advisory Committee found that registrar nameserver renaming practices had exposed over 500,000 gTLD domains to resolution hijacking risk as of September 2020, according to SAC125, the SSAC Report on Registrar Nameserver Management. In the cases we review, the same few mistakes recur: nameservers left pointing at a former provider, a DNS host account owned by a departed contractor, and no record of what the domain’s DNS looked like before a change. DNSSEC (DNS Security Extensions, which let resolvers verify that answers have not been altered) adds a cryptographic check on each level of delegation; our DNSSEC guide explains when it helps and where it does not.
How DNAccess Helps
Understanding how domain names and top-level domains fit into internet addressing is the first step toward controlling them. Our domain name management service documents where each domain is registered, which nameservers it uses and who controls the DNS host account, so a nameserver change or a lapsed delegation is caught before it becomes an outage or a hijacking.
This article is part of the DNAccess Domain Name Basics guides, which explain how domain names, registrars and DNS work in plain English.